Oh no, what happened to my OOHPod? Windows command prompt puts in a surprise appearance
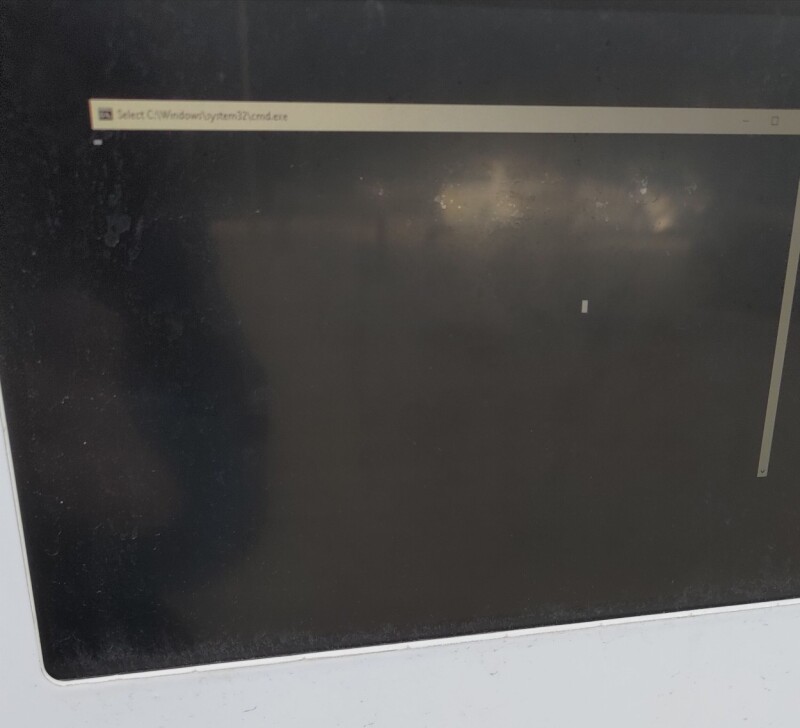
Pop quiz: somebody left a command shell logged in. What do you do?
The recent incident involving an exposed Windows command prompt on an OOHPod has significant implications for the app development community. This event highlights the importance of robust security measures, particularly when it comes to managing and securing access to development environments. The fact that a command shell was left logged in and accessible is a basic yet critical oversight that can lead to serious security breaches.
In the context of app development, especially within AI and agent economies, ensuring the security and integrity of development environments is paramount. This incident serves as a reminder of the potential vulnerabilities that can arise from seemingly minor lapses in security protocols. Developers and organizations must prioritize securing their environments, implementing strict access controls, and fostering a culture of security awareness among their teams.
As the industry moves forward, it's crucial for developers and organizations to review and enhance their security practices. This includes regular audits of access logs, implementing multi-factor authentication, and ensuring that all team members are trained on security best practices. Keeping a close watch on how this incident influences the development of more secure environments and the adoption of stricter security protocols will be key. The emphasis on security in app development is expected to grow, driving innovation in security technologies and practices.
Originally reported by theregister.com. AppNewsletter adds analysis for ai & agent economy readers.